What is vishing? Voice phishing, explained.
Vishing is voice phishing: a scam phone call or voicemail in which the caller impersonates a trusted party, such as a bank, a government agency or a relative, to extract money or login credentials. Phishing arrives by email and smishing by text message. Vishing arrives by voice, and AI voice cloning now lets the caller sound like someone you know.
What is vishing?
Vishing is a social engineering attack delivered by voice. The word blends "voice" and "phishing". The attacker calls, or leaves a scam voicemail, while pretending to be an organisation or a person the target trusts. The goal is the same as every phishing attack: get the target to hand over money, credentials or access before they stop to verify.
The US Cybersecurity and Infrastructure Security Agency (CISA) lists vishing alongside phishing and smishing as a core social engineering technique. The FTC counts it inside imposter scams, which have been the most reported fraud category in the United States every year since 2020 (FTC, June 2026).
Vishing works because a live voice is persuasive in ways text is not. The target cannot re-read a phone call. The caller controls the pace, interrupts doubts and keeps the target on the line until the money has moved. Caller ID spoofing makes the call appear to come from a bank's real number. AI voice cloning can make it sound like a real person.
In plain terms, vishing means a scam call. If someone phones claiming to be your bank, the IRS, Social Security, Microsoft, your boss or your grandchild, and wants a payment, a code or remote access right now, that is vishing.
If you are studying this for a security certification or writing awareness training, the formal definition, attack taxonomy and controls are in vishing in cyber security.
How does a vishing attack work, step by step?
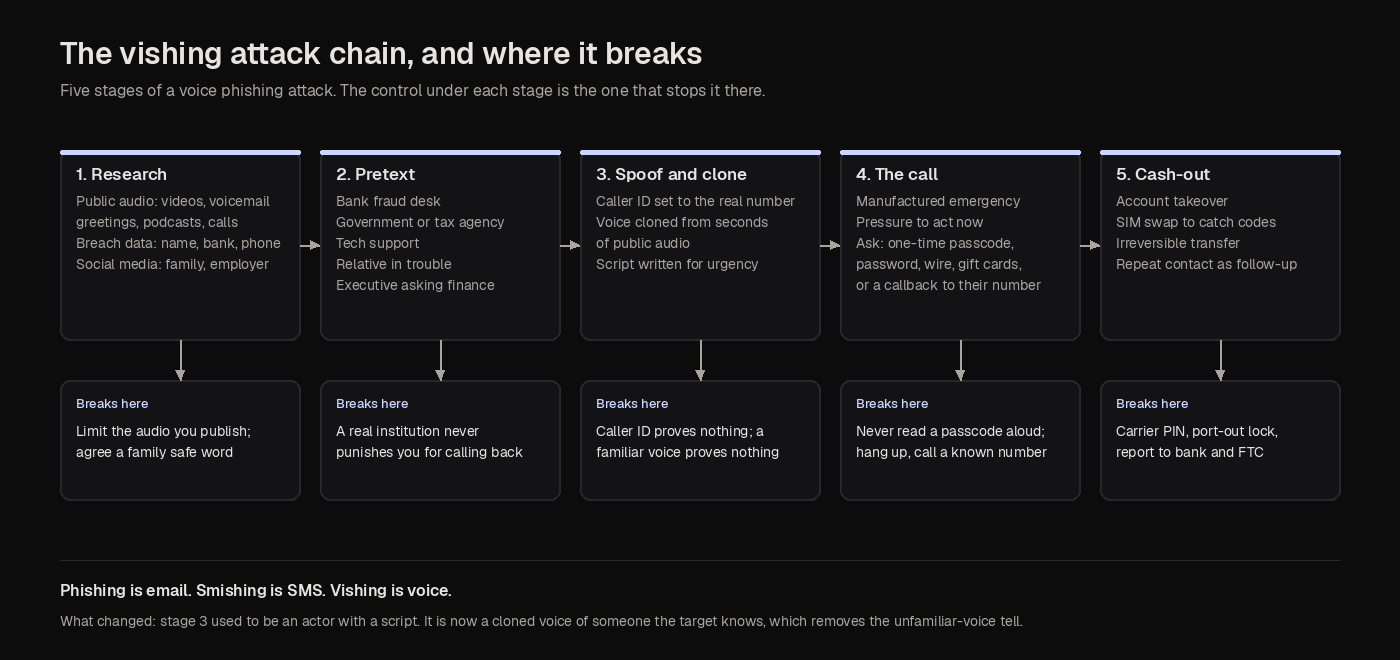
Nearly every vishing attack follows the same six-step sequence. Knowing the sequence is most of the defence, because the pressure only works while the target does not recognise the script.
- 01Reconnaissance. The attacker gathers a name, a phone number, a bank, an employer, or a relative's voice. Sources include data breaches, social media profiles, voicemail greetings and public video.
- 02Spoofing. The caller ID is forged to display a real institution's number or a known contact. The FCC describes caller ID spoofing as cheap and widely available, and illegal when used with intent to defraud.
- 03Pretext. The caller claims an identity: a fraud department, an IRS agent, an IT help desk, an executive, a grandchild in trouble. A cloned voice may back the claim up.
- 04Pressure. A crisis is manufactured: a fraudulent charge, an arrest warrant, a locked account, a confidential acquisition. The target is told to act now and tell no one.
- 05Extraction. The ask is something normal controls would block: a wire transfer, gift card codes, cryptocurrency, a one-time passcode, a password reset, or remote access to a device.
- 06Cash-out. Funds move through mule accounts or crypto within minutes. Bank transfers and payments carried the largest reported losses of any payment method in 2024, at $2 billion (FTC, March 2025).
What is the difference between vishing, phishing and smishing?
All three are phishing. The channel changes, the con does not. Email phishing, SMS smishing and voice vishing each impersonate a trusted party and manufacture urgency. The channel decides how fast the attack moves and which tells give it away.
| Attack | Channel | Typical pretext | What the attacker wants | The tell | What to do |
|---|---|---|---|---|---|
| Phishing | "Your account is suspended, log in here" | Credentials, malware install | Sender domain does not match the brand; link text does not match the URL | Do not click. Open the site from a bookmark or the official app. | |
| Smishing | SMS and messaging apps | "Unpaid toll", "package held", "unusual sign-in" | Card numbers, login details, small payments | Short link, unknown number, demand to pay through the link | Do not reply or tap. Check the account in the official app. |
| Vishing | Phone call or voicemail | "Fraud on your account", "a warrant has been issued", "I'm in trouble, I need help" | Wire transfer, gift cards, one-time passcode, remote access | Urgency plus secrecy; refusal to let you call back; a familiar voice you did not expect | Hang up. Call back on a number you already hold. |
The channels increasingly chain together. A smishing text about a "suspicious charge" tells you to call a number, and the vishing call does the extraction. In 2025, text messages were the most common contact method by report count, while phone calls accounted for 11% of fraud reports that involved a loss, behind websites or apps at 31% and social media at 28% (FTC testimony to the Joint Economic Committee, March 2026).
A fuller side-by-side, including how attackers chain a text and a call in the same attack, is in vishing vs smishing.
What are real examples of vishing?
Vishing scripts change with the news cycle, but the pretexts below account for most reported attacks. Each one targets a different fear.
Bank fraud department
"We've detected fraud on your account. Move your money to a safe account now." No bank asks this. Bank impersonators produced the highest losses of any business impersonation in 2025 (FTC, June 2026).
Government impersonation
The IRS, the Social Security Administration, Medicare or a court claims unpaid tax, a suspended Social Security number or an arrest warrant. People reported about $920 million lost to government impersonators in 2025 (FTC, June 2026).
Tech support
A "Microsoft" or "Apple" agent says your device is infected and needs remote access or a fee. Older adults reported $159 million lost to tech support scams in 2024 (FTC, December 2025).
Executive (CEO) fraud
A cloned executive instructs finance to wire funds urgently and confidentially. In 2024 an employee at the engineering firm Arup sent about US$25.6 million after a video call in which every other participant was a deepfake of a real colleague (CNN, May 2024). See CEO fraud.
Family emergency
A voice that sounds like a grandchild says there was a crash or an arrest and begs for bail money. The FTC warned in March 2023 that scammers can clone the voice from a short clip posted online (FTC consumer alert). See the grandparent scam.
One-time passcode theft
The caller "needs you to read back the code we just sent to stop a login". The code is the login. Reading it out hands over the account, and the real bank's text message makes the call feel legitimate.
IT help desk vishing
An attacker calls an employee posing as IT, or calls the help desk posing as an employee, to reset a password or enrol a new MFA device. CrowdStrike recorded a 442% rise in vishing operations between the first and second halves of 2024, most impersonating IT support (CrowdStrike Global Threat Report, February 2025).
Utility and delivery threats
"Your power will be disconnected within the hour unless you pay by prepaid card" or "a parcel is held, confirm your card details." The deadline is the weapon; the real utility sends written notice first.
Account verification
A call or voicemail asks you to "confirm" a password, PIN or security answers to keep an account open. Legitimate institutions already hold your details and never ask you to recite them on an inbound call.
Twelve documented cases, including the Arup video call, the Retool breach and the cloned-grandchild calls, are collected in real vishing examples. For the wider pattern across these scripts, see AI voice scams.
How has AI voice cloning changed vishing?
For most of its history, vishing relied on an unfamiliar voice and a believable script. The weak point was the voice. A stranger claiming to be your son did not sound like your son.
AI voice cloning removed that weak point. Commercial text-to-speech services such as ElevenLabs, and open-source models, can produce a convincing clone from a short sample of speech, and public audio is everywhere: voicemail greetings, podcasts, social video. The FTC's March 2023 alert described exactly this: a scammer clones a loved one's voice from a clip posted online, then calls with a fake emergency (FTC, March 2023).
Regulators moved. On 8 February 2024 the FCC released a unanimous Declaratory Ruling that AI-generated voices in robocalls are "artificial" under the Telephone Consumer Protection Act, making them illegal without prior consent and giving state attorneys general a direct route to prosecute (FCC, February 2024). In 2024 the FTC finalised its Impersonation Rule covering government and business impersonators (FTC, June 2026).
The scale followed. The FBI's 2025 Internet Crime Report included a section on artificial intelligence for the first time: 22,364 complaints and nearly $893 million in losses tied to AI-enabled schemes, including voice clones (FBI, April 2026).
For defence, this means one thing: you can no longer trust a voice because you recognise it. Verification has to happen out of band, by calling back on a number you already hold. A saved voicemail or recording can also be analysed for signs of synthesis, which is what an AI voice check does. It is one signal, not a substitute for the callback.
How common is vishing?
No agency publishes a vishing-only loss figure. Vishing is counted inside imposter scams and inside "phone call" as a contact method, so the honest answer is bounded by those numbers. Every figure below is reported losses; the figures count only people who filed a report, so the true total is higher.
| Statistic | Figure | Source and date |
|---|---|---|
| Total fraud losses reported to the FTC, 2025 | About $16 billion, up about 25% on 2024, the highest on record | FTC, June 2026 |
| Losses to imposter scams, 2025 | $3.5 billion, nearly three times 2020; the most reported fraud category since 2020 | FTC, June 2026 |
| Business and government impersonators, 2025 | Nearly $1 billion and about $920 million respectively | FTC, June 2026 |
| Share of loss reports that began with a phone call, 2025 | 11% (website or app 31%, social media 28%, email 10%, text 7%) | FTC testimony, March 2026 |
| Median loss when contact was by phone, 2024 | $1,500, the highest of any contact method | FTC, March 2025 |
| Internet crime losses reported to the FBI, 2025 | Nearly $21 billion across 1,008,597 complaints, up 26% on 2024 | FBI IC3, April 2026 |
| Losses reported by Americans over 60, 2025 | About $7.7 billion, up 37% on 2024 | FBI IC3, April 2026 |
| AI-enabled scam complaints, 2025 | 22,364 complaints, nearly $893 million | FBI IC3, April 2026 |
| Vishing operations, H1 to H2 2024 | Up 442%, most impersonating IT support | CrowdStrike, February 2025 |
What are the warning signs of a vishing call?
Any one of these is a reason to slow down. Two together, treat the call as hostile.
- 01Urgency plus secrecy. You are told to act now and to tell no one, so you cannot pause or verify.
- 02An unusual payment. A wire, gift cards, cryptocurrency, or a payment app transfer to someone you have never met.
- 03A request for a one-time passcode, password or PIN. No legitimate organisation asks you to read a code back to them.
- 04Caller ID that matches a real institution. Spoofing is trivial. A matching number proves nothing.
- 05A request for remote access to your computer or phone.
- 06A familiar voice saying unfamiliar things. Wrong details, odd phrasing, or a relative who insists you keep it from the rest of the family.
- 07Refusal to let you hang up and call back. A real institution is fine with you dialling the number on your card.
How do you protect yourself from vishing?
The defence is a habit, not a gadget. A cloned voice cannot survive a callback to a number you already trust.
Hang up and call back
Use the number on your card, your statement or the official website. Never a number the caller gives you, and never the number that just called.
Never share a one-time passcode
Banks and platforms send codes to you. They never ask you to read one back. A request for the code is the attack.
Agree a family code word
Anyone claiming an emergency must say it. Keep it off social media. Finance teams should do the same for payment changes.
Treat caller ID as decoration
US carriers run the FCC's STIR/SHAKEN caller authentication, which flags some spoofed calls, but a matching number is still not identity. Verify through a channel you opened.
Slow the money
Set transfer limits and alerts on personal accounts. For businesses, require dual approval and a callback to a known number for any new payee or changed bank details.
Check the recording
If a voicemail or recording is driving the decision, save it and run it through an AI voice detector. A synthetic result is grounds to stop. An authentic result is still not grounds to pay.
For organisations, two controls close most of the gap: the help desk verifies identity before any password or MFA reset, and security awareness training includes recorded vishing calls, not only email phishing tests. Fraud teams can see how recorded audio is checked at scale on the fraud detection page.
The full checklist, including family code words, SIM-swap protection and what to do if you have already paid, is in how to protect yourself from vishing.
What should you do if you were targeted by vishing?
Speed matters more than embarrassment. Most recoveries happen in the first hours.
- 01Stop contact. Hang up. Do not call the number back, and do not answer follow-up calls from it.
- 02If money moved, call your bank now. Use the number on your card. Ask for a recall of the wire or payment and a block on the account. Report gift card codes to the card issuer.
- 03If you shared a code or password, change the password, sign out all sessions and turn on multi-factor authentication, from a device you trust.
- 04If you gave remote access, disconnect the device from the internet, run a malware scan, and change passwords from a different device.
- 05Report it. In the US: the FTC at ReportFraud.ftc.gov; the FBI at IC3 for any financial loss; the FCC at consumercomplaints.fcc.gov for spoofed or robocalls; and local police if you need a report number. Elsewhere: Action Fraud (UK), the Canadian Anti-Fraud Centre, Scamwatch (Australia).
- 06Preserve evidence. The number, the time, the voicemail, any texts or emails that preceded the call. Investigators and banks ask for all of it.
- 07Warn the people around you. Vishing crews recycle lists. A relative or a colleague is often the next call.
Common questions about vishing
What does vishing mean?
What is an example of vishing?
What is the difference between vishing and smishing?
What does vishing stand for?
What is a vishing attack?
What is a common tactic used in vishing attacks?
Is vishing illegal?
Can AI detect a vishing call?
How do I report vishing?
Got a voicemail that felt off? Check the voice.
Save the recording and run it through the AI voice detector. Free for a single check, no account needed. Then make the callback anyway.